A large number of failed logon attempts within a short span of time usually indicates a security threat. This is why, it is essential for administrators to keep an eye out for such events and get to the root of the source of the failed logons. This article takes you through the steps of how to perform failed logon auditing using Microsoft's native tools.
Tracking the Source of Failed Logon Attempts
Run gpmc.msc to open the Group Policy Management Console.
In the Group Policy Management Editor, edit the domain’s Default Domain Policy by right-clicking on it.
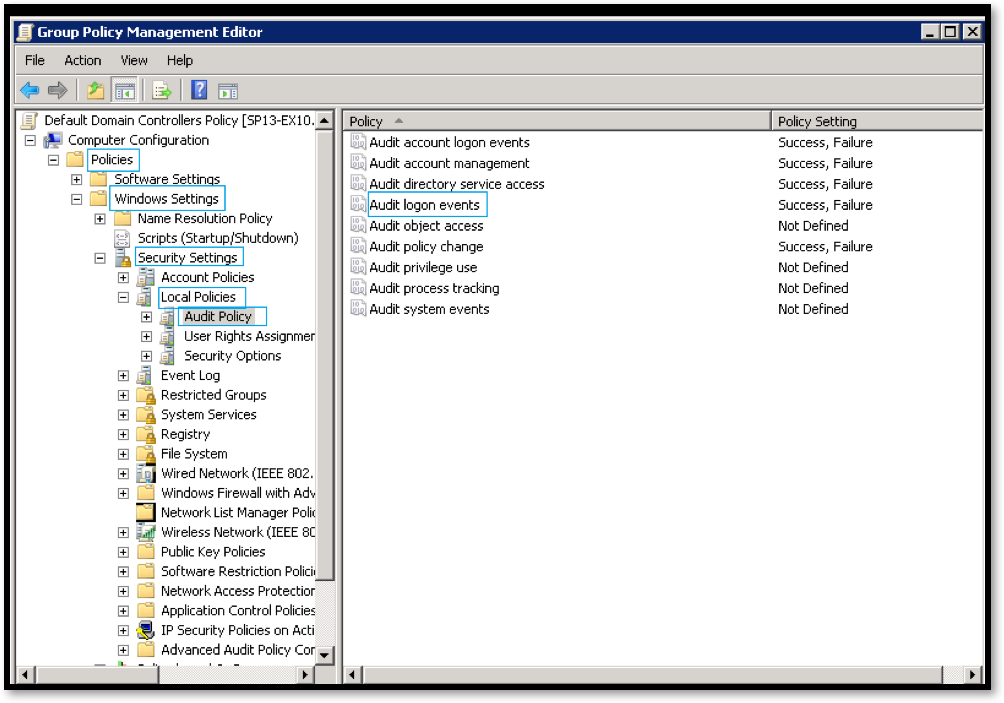
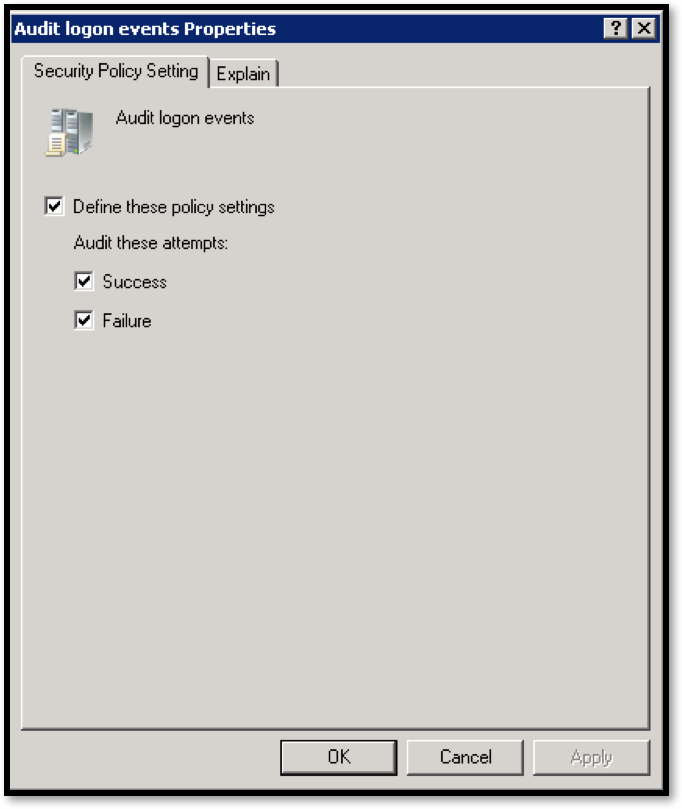
Navigate to Computer Configuration > Windows Settings > Security Settings > Local Policies > Audit Policy and double-click Audit Logon Events.
Open the Command Prompt and run the command gpupdate/force to update Group Policy.
To get to know about the failed logon events, filter the Security Event Log for Event ID 4625.
Double-click on any event to see details of the source from where the failed logon attempts originated.